HackTheBox Web Challenges

Templated Dificulty: easy Description: Can you exploit this simple mistake? Solution First we visit the site and see that uses jinja2, this template is susceptible to SSTI attacks. We see that the directory searched is rendered in the page with 25, so its vulnerable to SSTI. We use the payload that will allow us to RCE on the server to read the file flag.txt, we extract it from PayloadsAllTheThings. ...
July 1, 2022 · 2 min · 284 words · Jesus Lujan

Os Command Injection Labs

OS command injection allows an attacker to execute arbitrary operating system (OS) commands on the server that is running an application, and typically fully compromise the application and all its data. OS command injection, simple case This lab contains an OS command injection vulnerability in the product stock checker. The application executes a shell command containing user-supplied product and store IDs, and returns the raw output from the command in its response. ...

June 10, 2022 · 4 min · 771 words · Jesus Lujan

Cross Site Scripting (XSS)

Cross-site scripting known as XSS is a web vulnerability in which malicious scripts are injected int benign and trusted websites. XSS occur when an attacker send malicious code in any user input fields in a browser to a different end-user. Mechanisms In an XSS attack the attacker inject script in HTML code so you’ll have to know javascript and HTML syntax, wbe uses scripts to control client-side application logic and make the website interactive, for example this script generates Hello! pop-up on the web page: ...

May 18, 2022 · 3 min · 484 words · Jesus Lujan

Cyber Apocalypse 2023 2x Web Challenges Writeup

Kryptos Support Checking the web page of this challenge gives a form to send an issue and an admin will review that issue. So its interesting, maybe the admin will click in that issue and we can inject some kind of payload, like an stored xss, these approach is similar to the bankrobber box in htb. So we can craft the payload to steal the cookie of the admin or the user who will review out ticket. ...

May 18, 2022 · 2 min · 381 words · Jesus Lujan

Directory Traversal Labs

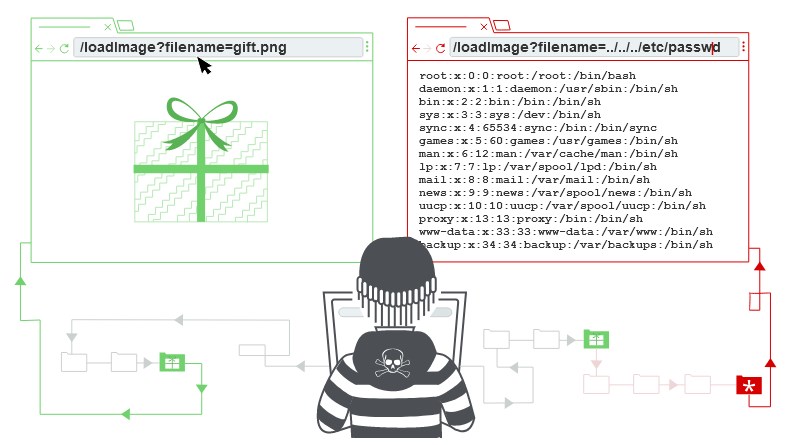
Also known as file path traversal allows to read arbitrary files on the servers. in some cases an attacker might be able to write arbitrary files on the server, allowing them to modify application data or behavior. Reading arbitrary files via directory traversal We can use the .. characters to access the parent directory, the following strings are several encoding that can help you bypass a poorly implemented filter. For example the url takes a filename parameter and returns the content of the file, the aplicaciones appends the requested filename to this base directort and uses an API to read the contents, so the application implements no defenses against directory traversal attacks,so an attacker can request the following URL to retrieve an arbitrary file from the server’s filesystem: ...

May 10, 2022 · 4 min · 852 words · Jesus Lujan